Project: OWASP Top 10
Historical development, architectural differences, and industry alignment of OWASP Top 10 projects covering Web, Mobile, API, K8s, CI/CD, and LLM/Agentic systems.
Historical development, architectural differences, and industry alignment of OWASP Top 10 projects covering Web, Mobile, API, K8s, CI/CD, and LLM/Agentic systems.
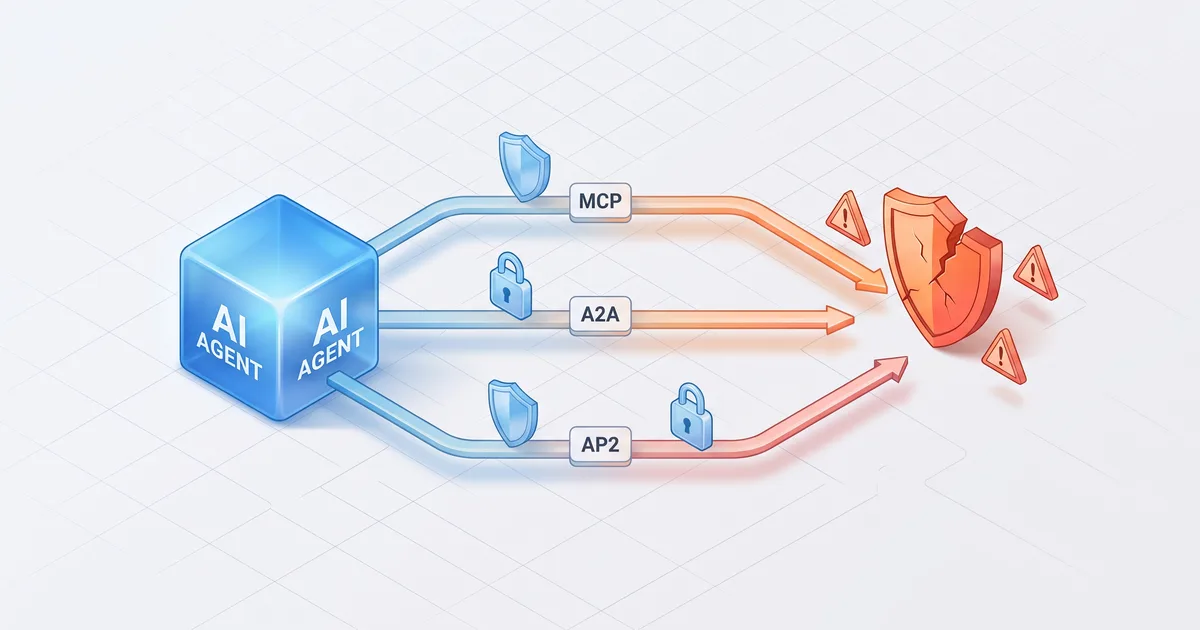
As autonomous AI agents move into production, protocols like MCP, A2A, and AP2 form the new digital backbone. But what happens when we give models execution privileges? Let's break down the attack surfaces layer by layer.
The Go (Golang) programming language for cybersecurity researchers, building fast network scanners, exploit development, and offensive tool design.
Balancing Shift-Left and Shift-Right paradigms across the SDLC: Enterprise CI/CD pipeline security, GitOps isolation, and eBPF-powered runtime observability.
Reclaiming data sovereignty in modern computing paradigms: sovereign technologies like LaTeX, DuckDB, Slidev, Nextcloud Hub, OnlyOffice, Mailcow, and Enterprise Linux.
A comprehensive architectural guide exploring modern web rendering strategies (CSR, SSR, SSG, ISR), tech stacks (MERN, PERN, .NET), and DevSecOps supply chain security.
A technical evaluation of SentinelOne Singularity Platform covering autonomous agent architecture, Storyline™ correlation model, VSS-based rollback mechanisms, and Purple AI telemetry from a SOC engineering perspective.
A comprehensive cyber threat intelligence guide combining classic OSINT and network reconnaissance with cloud exposure, supply chain analysis, AI-powered CTI pipelines, and the ProjectDiscovery ecosystem.
Global Advanced Persistent Threat (APT) groups, their strategic motivations, TTPs, and MITRE ATT&CK mapping: comprehensive analysis of state-sponsored actors from Russia, China, Iran, and North Korea.
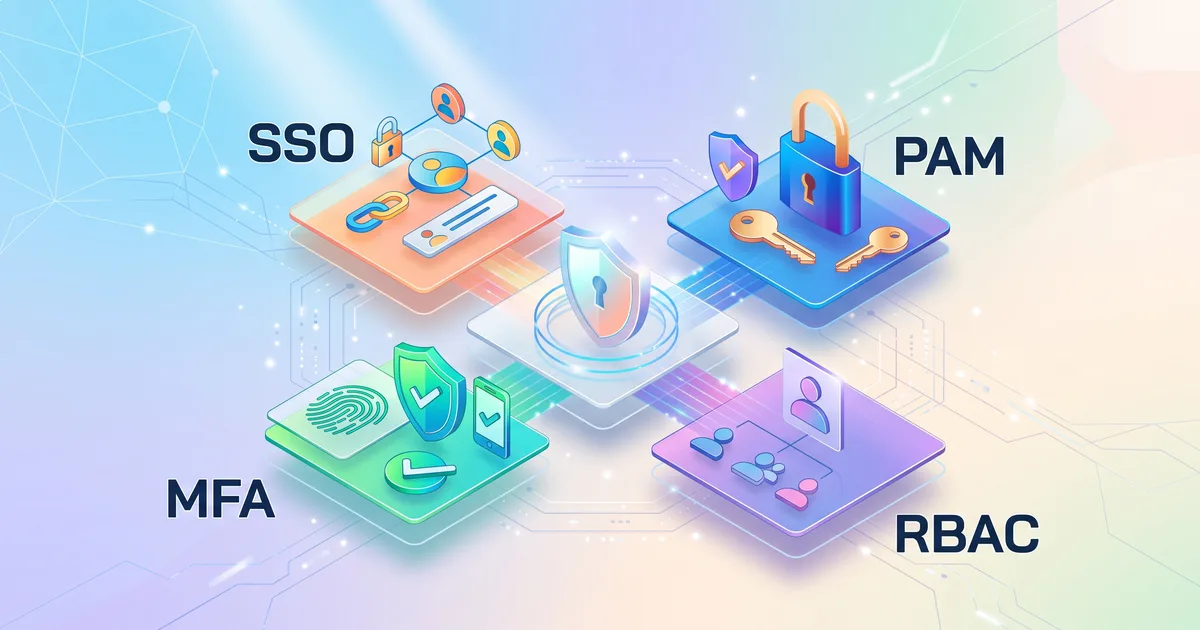
A comprehensive guide to Identity and Access Management (IAM) at the core of Zero Trust: exploring SSO, MFA, PAM, RBAC/ABAC models, and modern federation protocols.
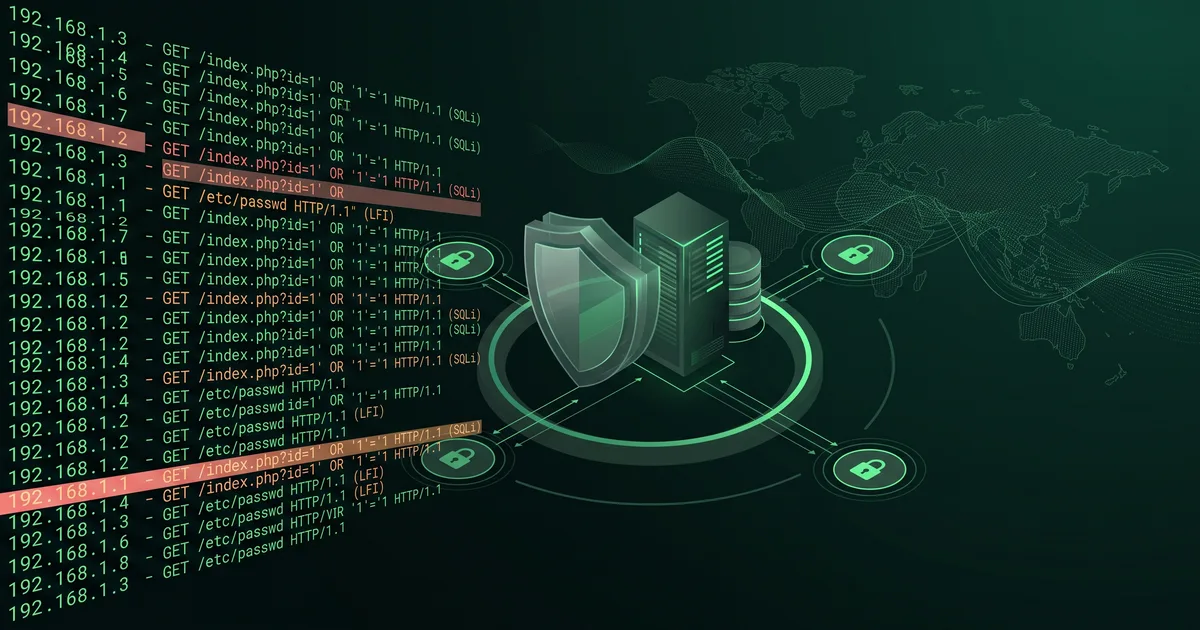
A comprehensive guide on detecting web application attacks (SQLi, XSS, LFI, RFI, Path Traversal) by analyzing Apache access logs manually and automatically using ModSecurity and Fail2Ban.
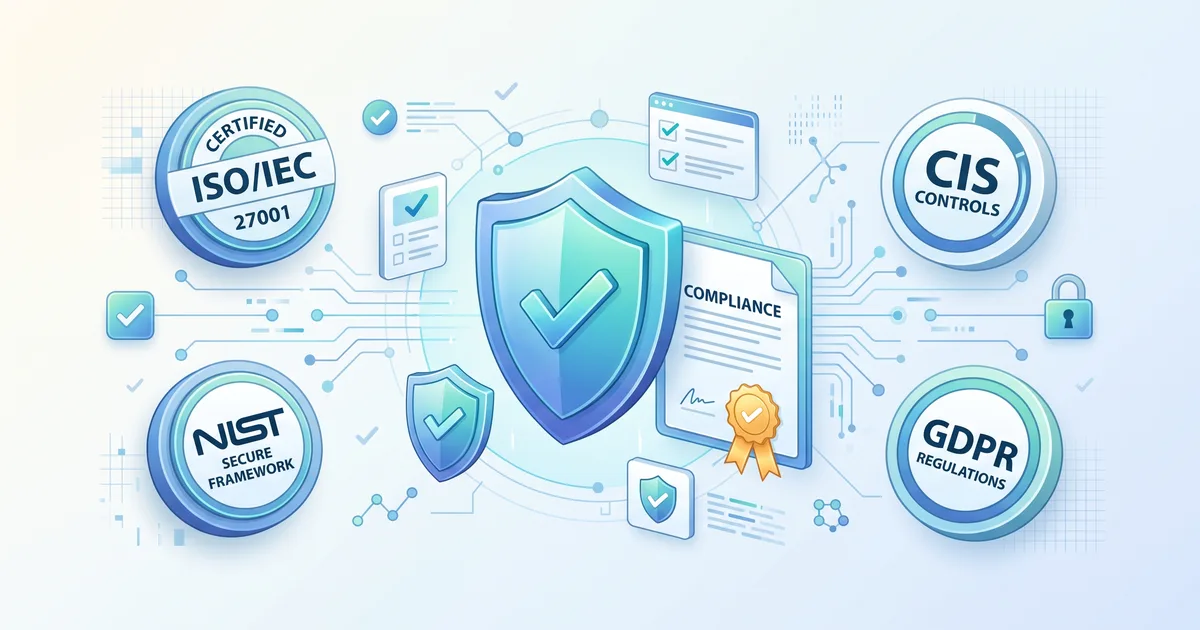
A comprehensive guide to international information security standards (ISO/IEC 27001, NIST, CIS), regulatory frameworks, and cybersecurity certification bodies.
A comprehensive guide to Windows system administration, essential CMD and PowerShell commands, MMC management consoles, Active Directory administrative tools, and WMI.
Architectural, telemetry, and operational analysis of leading enterprise EDR/XDR solutions including CrowdStrike, SentinelOne, Microsoft Defender, and Trend Micro.
A comprehensive guide to penetration testing distros, digital forensics (DFIR), malware analysis, privacy platforms, and simulated Active Directory labs (GOAD, DetectionLab, Attack Range).
A comprehensive security guide examining how an attacker maintains persistence after Initial Access and spreads laterally through the network. Covers WMI Event Subscriptions, COM Hijacking, IFEO, Kerberos attacks, SOC detection engineering, and hardening steps.
A comprehensive guide to installing, configuring, and managing Elasticsearch, Logstash, Kibana, and Beats (Elastic Stack) on Debian/Ubuntu, including Elastic Agent/Fleet architecture, ES|QL query language, Vector Database integration, and MITRE ATT&CK SIEM rules.
An in-depth guide to operating system structures, processes, CPU scheduling algorithms, memory management (segmentation, paging, virtual memory), and security fundamentals, inspired by the classic 'Dinosaur Book' (Operating System Concepts).
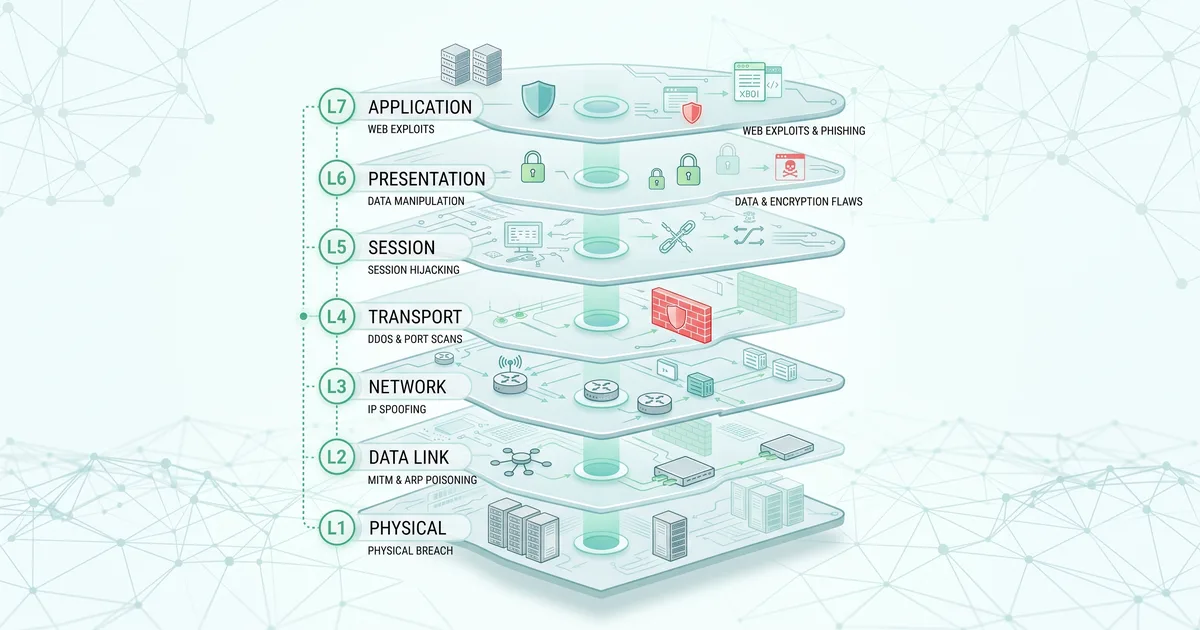
From physical sniffing and ARP poisoning to SYN floods, BGP hijacking, and Layer 7 exploits: an engineering breakdown of attacks and defenses across all seven OSI layers.
From ancient scytale cylinders to elliptic curves, Diffie-Hellman handshakes, blockchain consensus, and practical Java implementations: your definitive guide to cryptology.
A complete guide to malware analysis fundamentals: malware taxonomy, building an isolated sandbox lab, static and dynamic analysis, memory forensics with Volatility, and reverse engineering tools.
An architectural overview of Kali Linux, deployment strategies, the penetration testing lifecycle, and practical offensive security toolchains.
A comprehensive guide to system programming with C and x86 Assembly. Explore processor architecture, low-level memory management, and hardware integration through theory and practical laboratory exercises.
A comprehensive guide on Python programming for security professionals, covering HTTP requests scripting, web automation with Selenium, socket programming for port scanning, and SSH remote management using Paramiko.
From ENIAC's tangle of cables to Xerox PARC, Unix wars, Linux, and modern cloud native ecosystems: the remarkable evolution of operating systems.